Collaboration
AWS WickrGov
Continuous, attribute-based access control for WickrGov rooms. Virtru checks who can join each room, and keeps checking for as long as they stay.
Mission-critical communications with real-time access governance
Rocket.Chat runs secure messaging across classified networks. Data Harbor Platform keeps every channel membership in line with current clearance.
How Rocket.Chat and Data Harbor Platform work together, and what each one does.
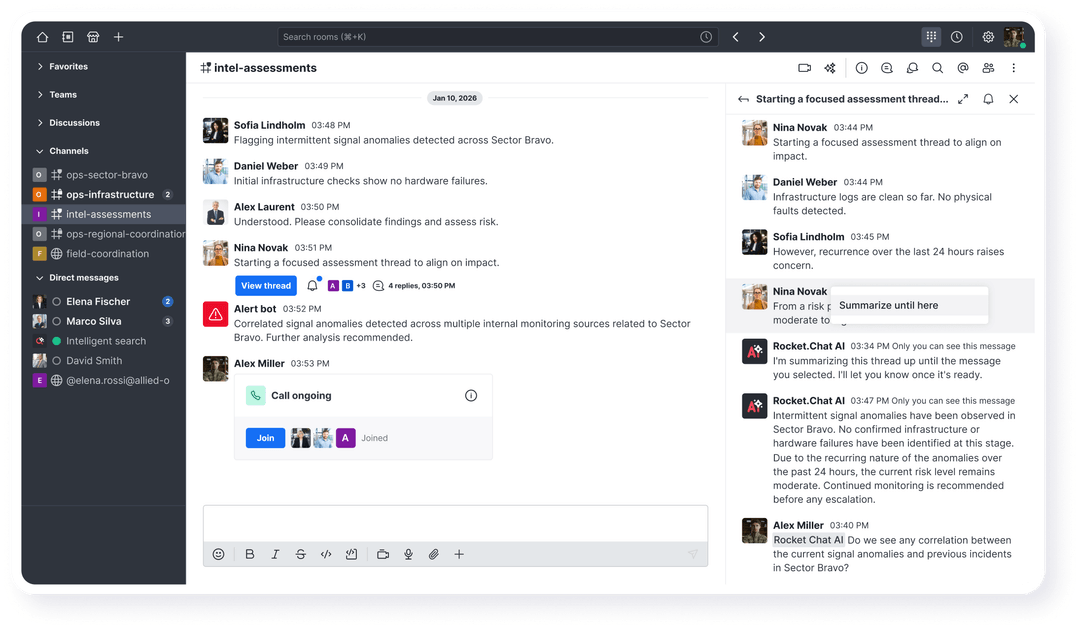
Rocket.Chat is the secure communications platform for organizations with the highest security and compliance requirements. Deployed across NIPRNet, SIPRNet, and JWICS, Rocket.Chat holds DoW Authorization to Operate at Impact Level 6 and is listed in the AWS Intelligence Community Marketplace.
Defense agencies, intelligence community organizations, and allied partners rely on Rocket.Chat for mission-critical coordination across classification boundaries. The platform provides native attribute-based access control (ABAC) with open architecture, sovereign deployment options, and the operational discipline that classified environments require.
How it works together
With Virtru Data Harbor Platform, Rocket.Chat extends channel access governance from provisioning-time decisions to continuous, automated, real-time policy enforcement. The integration delivers an external decision layer that evaluates every channel membership against current entitlements sourced directly from authoritative identity providers.
The result is identity-driven enforcement without vendor lock-in, complete auditability that persists beyond the collaboration boundary, and the decision-level evidence that IG auditors and Zero Trust assessors require.
Where they connect
Rocket.Chat queries Virtru Data Harbor Platform at configurable intervals to validate every channel membership against current identity provider entitlements. When an analyst’s compartmented clearance expires, or an engineer rotates from Program TITAN to Program APOLLO, the identity provider update propagates to the Data Harbor Platform, which informs Rocket.Chat to automatically remove access, typically within minutes, not days. This continuous validation eliminates residual access gaps created by traditional static roster approaches.
The Data Harbor Platform serves as a central policy decision point, evaluating entitlements without storing raw identity data in Rocket.Chat’s collaboration environment. Rocket.Chat sends minimal context, user identifier and channel policy requirements, and receives an authoritative Allow or Deny decision. This architectural separation preserves identity sovereignty while adding data-layer enforcement. User entitlements remain in the organization’s IdP; no raw entitlement data crosses into the collaboration platform.
What you get when Rocket.Chat and Data Harbor Platform run side by side.
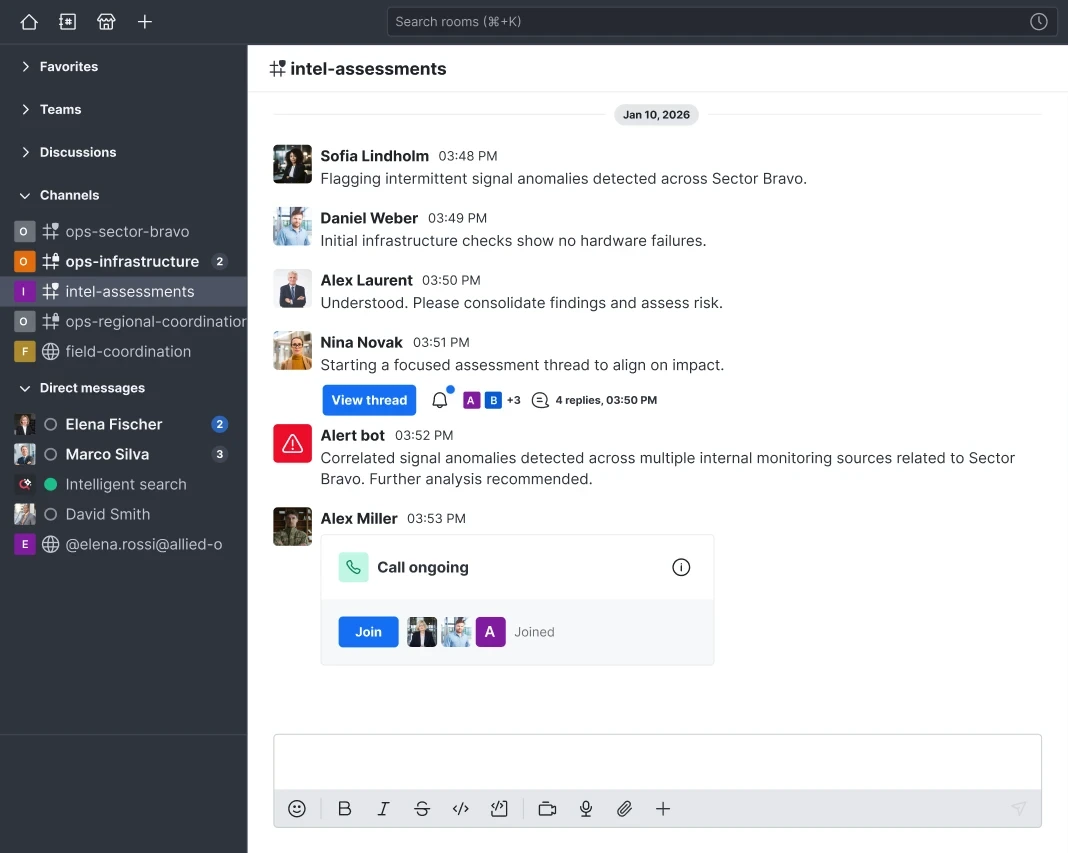
Provides automated channel membership updates that respond to entitlement changes within minutes, eliminating residual access gaps.
Ensures users without assigned entitlements cannot be added to rooms and preserves existing memberships when entitlement data is unavailable.
Evaluates entitlements from any OIDC/OAuth2-compatible provider while adding necessary data-layer enforcement.
Prevents room owners from adding unauthorized users by validating all manual changes against current entitlements.
Automates channel dissolution during program rotations or task force stand-downs, removing the need for manual administrative cleanup.
Provide comprehensive logging of every access decision, providing the evidentiary record required for Zero Trust monitoring and IG audit compliance.
Deploying Virtru Data Harbor Platform with Rocket.Chat for ABAC-managed channels requires active deployments of both platforms and an identity provider to source the entitlements that govern access decisions.
Supported across NIPRNet, SIPRNet, and JWICS; on-premises, customer cloud, or air-gapped environments.
Customer VPC or on-premises; matched to Rocket.Chat’s deployment profile and accreditation boundary.
Okta, Microsoft Entra ID, Ping Identity, or equivalent OIDC/OAuth2-compatible identity system holding clearance, program, department, and nationality attributes.
Per-room entitlement policy defined by authorized admin in Rocket.Chat (e.g., clearance_level = TOP_SECRET AND project_assignment = OLYMPUS).
Between Virtru Data Harbor Platform and Rocket.Chat services, within the accreditation boundary of the classified network.
How the two platforms split the work across security, compliance and privacy.
Security architecture
The joint solution applies separation of duties across the access decision chain. Your identity provider is the authoritative source of identity entitlements. Virtru Data Harbor Platform is the external decision engine, Rocket.Chat sends only the minimum required data and receives an Allow or Deny response. Rocket.Chat enforces the decision and logs the outcome. No user entitlement data is ever stored in the collaboration platform.
The system fails secure by default: users without assigned entitlements cannot be added to rooms, and existing memberships are preserved unchanged when entitlement data is unavailable.
Compliance and standards
Virtru Data Harbor Platform and Rocket.Chat can be operationally deployed across NIPRNet, SIPRNet, and JWICS. The integration supports NIST SP 800-162 for Attribute-Based Access Control and NIST SP 800-207 for Zero Trust continuous validation requirements.
Virtru’s Trusted Data Format (TDF) is an open standard for persistent data protection. Virtru Data Harbor Platform is built on OpenTDF, the open-source foundation Virtru created and continues to lead. Rocket.Chat utilizes the Matrix protocol for chat standards, XMPP (Extensible Messaging and Presence Protocol), and OMEMO for end-to-end encryption on XMPP.
Privacy and data sovereignty
Identity entitlements remain in your organization’s identity provider. Virtru Data Harbor Platform evaluates entitlements from any OIDC/OAuth2-compatible IdP, preserving identity sovereignty while adding data-layer enforcement. Policy decisions are logged with comprehensive audit context, but raw entitlement values never persist in the collaboration environment.
Collaboration
Continuous, attribute-based access control for WickrGov rooms. Virtru checks who can join each room, and keeps checking for as long as they stay.
Collaboration
Sovereign video meetings, governed end to end. Virtru checks policy when a meeting is scheduled, and again as each person joins the call.
Collaboration
Secure Matrix-based messaging with access that follows policy. Virtru governs who can join each room, and who can open the files shared inside it.