Collaboration
Pexip
Sovereign video meetings, governed end to end. Virtru checks policy when a meeting is scheduled, and again as each person joins the call.
Sovereign communications with fine-grained data governance
Element runs sovereign, end-to-end encrypted communications. Data Harbor Platform decides who can join each group and open each file.
How Element and Data Harbor Platform work together, and what each one does.
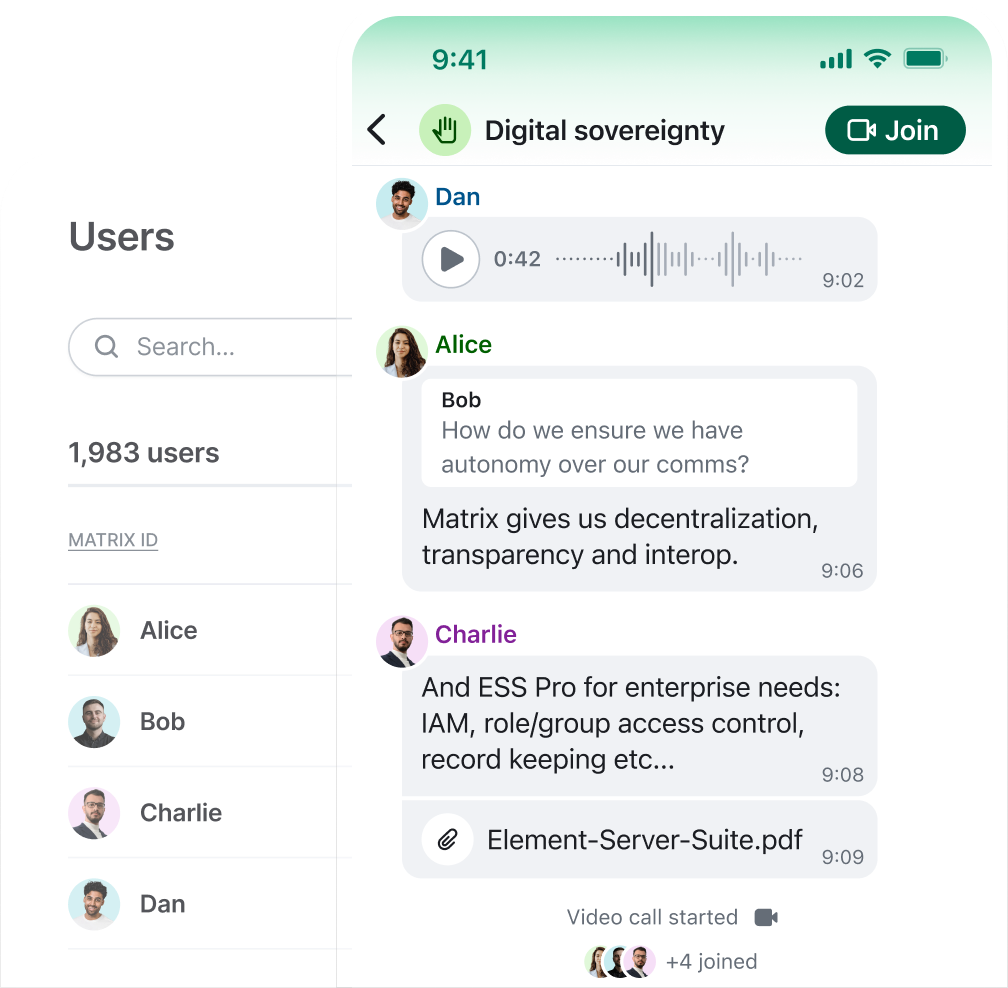
Element provides digitally sovereign, decentralized, and secure communications built on the Matrix open standard, which is independently governed by the Matrix Foundation. Trusted by defense, intelligence, and government agencies in over 35 countries, including the German Bundeswehr, NATO ACT, the U.S. Department of War, and the United Nations, Element offers end-to-end encrypted messaging, voice, video, and file sharing with self-hosted options that meet the strictest national sovereignty requirements. The Element Server Suite Pro (ESS Pro) delivers enterprise-grade identity management, group-synchronized access control, and audit logging to support organizations operating at the highest security levels.
The Virtru Data Harbor Platform brings fine-grained data governance to Element’s sovereign communications. By integrating Element’s messaging fabric with Virtru’s Policy Decision Point (PDP), organizations gain persistent, attribute-based access controls for all group memberships and shared files. During user interaction, the PDP assesses real-time entitlements, such as security clearance, program assignment, and nationality, to provide instant access decisions.
Element’s Policy Enforcement Point (PEP) operates alongside the Element Homeserver, implementing the Matrix Policy Server protocol (Matrix Spec Change 4284). When a user joins a group, the PEP validates the request against the Virtru PDP using entitlements like clearance level and program assignment. If an analyst’s clearance expires or a user changes programs, updates propagate from the identity provider to the Virtru platform, triggering Element to automatically revoke access, typically within minutes. This continuous validation eliminates the gaps often found in static group membership models.
Virtru preserves Element’s infrastructure, group structures, and identity configurations while adding a crucial governance layer to maintain continuous data security.
What you get when Element and Data Harbor Platform run side by side.
Automatically validates group membership against real-time identity entitlements to ensure seamless updates when clearance levels or program assignments change.
Maintains consistent governance across complex networks by instantly re-evaluating access policies whenever user entitlements shift without manual intervention.
For documents shared within an Element room. The Virtru platform compares the document’s embedded NATO STANAG 4774 classification labels against the entitlements of every member present in the room.
Blocks users lacking valid entitlements from group entry while ensuring existing access remains static rather than permissive during data outages.
Capture comprehensive audit trails for every security decision, including group joins, file interactions, and access denials, to support national security oversight.
Leverages the Matrix Policy Server protocol to seamlessly connect Element’s messaging fabric to Virtru’s central policy decision point.
Deploying fine-grained data governance at the message and file layer in an Element environment requires active deployments of both platforms, a configured Homeserver Policy Enforcement Point, and an authoritative Identity Provider sourcing the entitlements that govern access decisions.
Provides the Element Homeserver managing user accounts, groups, and messages, and the Element Clients that users interact with; supports on-premises and sovereign cloud deployments across national classified networks and partner federation environments.
The Element-side integration component deployed alongside the Homeserver that evaluates every group join request against the Virtru PDP before access is granted; implements the Matrix Policy Server protocol (Matrix Spec Change 4284).
Customer VPC or on-premises within the accreditation boundary; serves as the Policy Decision Point evaluating group access requests from the Homeserver PEP.
Microsoft Entra ID, Ping Identity, or equivalent OIDC/OAuth2-compatible identity system holding clearance, program assignment, department, and nationality attributes the PDP evaluates at every access decision.
Per-group entitlement policy defined by authorized administrator and referenced by the PDP at every group access and file access decision.
Between Virtru Data Harbor Platform and Element homeserver services, within the accreditation boundary; the Homeserver PEP transmits only the minimum data required for each policy decision and receives an Allow or Deny.
How the two platforms split the work across security, compliance and privacy.
Security architecture
The joint solution secures data by enforcing a strict separation of duties across all layers. While the Element Homeserver manages user accounts, groups, and messaging, the Homeserver Policy Enforcement Point (PEP) acts as an intermediary, intercepting group join requests and validating them against the Virtru PDP before granting access. Entitlement values are sourced exclusively from the organization’s Identity Provider; the Virtru PDP receives only the minimum data required to issue an “Allow” or “Deny” decision, ensuring that no sensitive entitlement data is ever stored within the Element environment.
The system is designed to fail secure: users without valid entitlements are denied group access, and in the absence of entitlement data, existing memberships remain unchanged. Similarly, file access is denied if entitlement values are missing or incomplete, preventing any permissive fallback.
Compliance and standards
This integration aligns with NIST SP 800-162 for attribute-based access control and NIST SP 800-207 for Zero Trust Architecture, while incorporating STANAG 4774 security labels to support NATO coalition operations. By connecting Virtru’s data governance layer to these frameworks, the solution ensures interoperability across classified allied environments.
The architecture is built on open standards: Virtru’s Trusted Data Format (TDF) and OpenTDF, evolved from NSA-developed technology, provide persistent protection, while Element leverages the Matrix open standard for decentralized communication. By implementing Matrix Spec Change 4284, the Homeserver PEP directly contributes to this open ecosystem.
Privacy and data sovereignty
Identity sovereignty is preserved by keeping entitlements within your organization’s existing IdP. The Virtru Data Harbor Platform evaluates these entitlements from any OIDC/OAuth2-compatible source, with the Homeserver PEP transmitting only the minimum data necessary for each decision. No raw entitlement values persist in the Element environment. Furthermore, because ZTDF binds access policies to the data object itself, enforcement occurs at the Key Access Service layer, ensuring file governance persists across federation boundaries without storing policy logic on partner homeservers.
Collaboration
Sovereign video meetings, governed end to end. Virtru checks policy when a meeting is scheduled, and again as each person joins the call.
Collaboration
Mission-ready collaboration with Zero Trust file protection. A Virtru plugin decides who can upload and view files in each channel, wherever they travel.
Collaboration
File sanitization paired with policy controls. Glasswall rebuilds each file clean, and Virtru keeps it encrypted and governed as it crosses domains.