Collaboration
Rocket.Chat
Channel access that keeps up with your team. Virtru checks members against your identity provider, and revokes access once they no longer qualify.
Policy-enforced meeting access for classified programs
Pexip runs sovereign video for classified networks. Data Harbor Platform checks clearance when a meeting is scheduled and again at the door.
How Pexip and Data Harbor Platform work together, and what each one does.
Pexip Secure Meetings provides self-hosted, sovereign video teleconferencing designed for defense and government organizations operating across NIPRNet, SIPRNet, JWICS, and tactical environments. Built on the 100% software-based Pexip Infinity platform, the solution operates independently of third-party infrastructure and is certified by DISA for DoD Impact Levels 4 through 7, including FedRAMP authorization. From ministerial discussions to cross-domain planning, Pexip ensures secure collaboration where sensitive mission data cannot traverse uncontrolled infrastructure.
How it works together
The integration of Pexip Secure Meetings and the Virtru Data Harbor Platform transforms meeting governance by replacing static invite management with continuous, attribute-based policy enforcement. By adding an external policy decision layer, the combined solution evaluates every scheduling and join request against real-time entitlements sourced directly from your authoritative identity provider.
This partnership delivers seamless integration without replacement. Virtru enhances Pexip’s secure infrastructure by adding an attribute-driven decision layer that remains auditable and policy-enforced, allowing organizations to maintain their existing identity and video workflows while significantly hardening their security posture.
Where they connect
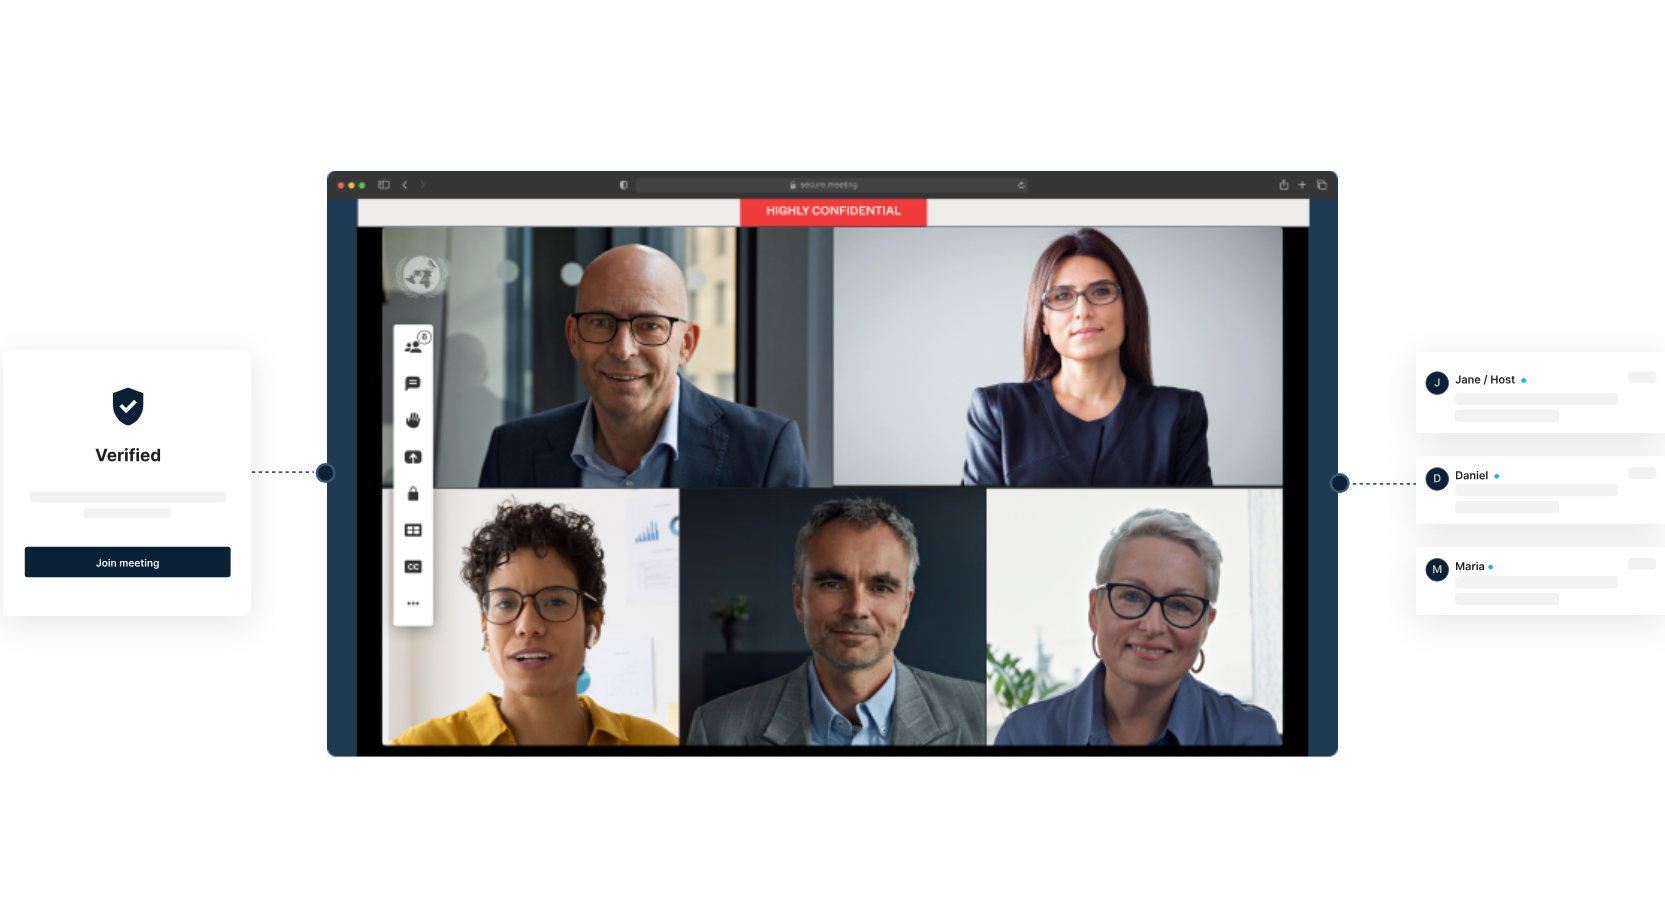
Move beyond one-time invite validation to a Zero Trust model where access is verified at the moment of scheduling and again at the moment of entry.
When an organizer creates a meeting, Pexip queries Virtru to surface only the classification levels and need-to-know designations that the organizer is entitled to hold. This ensures meetings are never scheduled at a level higher than an organizer’s verified clearance.
Participant entitlements are re-evaluated in real time when they attempt to enter a meeting. Any changes to clearance status or program rotations that occurred after the initial invite was sent are caught at the door, closing the security gaps left by traditional static lists.
What you get when Pexip and Data Harbor Platform run side by side.
Ensures meeting classification is policy-enforced by querying the Virtru Authorization Service to restrict scheduling options to the organizer’s verified entitlements.
Block participants lacking required entitlements from the invite list at scheduling time by automatically validating invitees against the meeting’s access attributes.
Validates participant entitlements in real-time at the moment of entry to account for clearance changes, suspensions, or rotations that occurred after the invite was sent.
Centralizes scheduling and join access decisions using the Virtru platform to enforce uniform organization-wide policies without requiring per-meeting configuration.
Denies meeting access and scheduling permissions when entitlement data is unavailable or unsupported, ensuring the system never defaults to open access.
Provide continuous, granular evidence trails for Zero Trust assessors by logging every scheduling, invite, and access decision with full context.
Deploying Virtru Data Harbor Platform with Pexip Secure Meetings to enforce attribute-based access control at scheduling and join requires active deployments of both platforms and an Identity Provider to source the entitlements that govern access decisions.
Self-hosted deployment; supports on-premises, air-gapped, and hybrid cloud environments; supported across NIPRNet, SIPRNet, JWICS, and tactical network environments at DoD Impact Levels 4 through 7.
The Pexip-built integration component including the OWA add-in that enforces ABAC at meeting scheduling and the join-time enforcement component that evaluates participant entitlements at meeting entry.
Customer VPC or on-premises; matched to Pexip’s deployment profile and accreditation boundary.
Okta, Microsoft Entra ID, Ping Identity, or equivalent OIDC/OAuth2-compatible identity system holding clearance, program assignment, releasability, and need-to-know attributes.
Per-meeting classification and releasability policy defined by authorized administrator and referenced at every scheduling and join decision.
Between Virtru Data Harbor Platform and Pexip services, within the accreditation boundary of the classified network.
How the two platforms split the work across security, compliance and privacy.
Security architecture
The joint solution establishes a clear separation of duties across the entire VTC access decision chain. Within this framework, your identity provider remains the authoritative source of identity entitlements, while the Virtru Data Harbor Platform serves as the external decision engine. During operation, the Pexip Policy Enforcement Point calls the Virtru Authorization Service with only the minimum required data to receive a definitive Allow or Deny response. Pexip then enforces this decision and logs the outcome, ensuring that no sensitive entitlement data is ever stored within the Pexip meeting platform itself.
By design, the system fails secure to prevent unauthorized access under any circumstances. Users without assigned entitlements are blocked from joining meetings, and organizers are restricted from scheduling sessions at classification levels that exceed their verified credentials. This fail-secure logic also applies when entitlement data is temporarily unavailable; the system defaults to a Deny response rather than failing open. Consequently, an organizer cannot create a classified meeting if entitlements cannot be evaluated, and participants are denied entry if their status cannot be verified at the moment of join.
Compliance and standards
Pexip Secure Meetings is fully certified by DISA on the DoDIN APL and UC APL, and it is FedRAMP Authorized for government cloud deployments. The platform utilizes FIPS 140-2/140-3 validated encryption and maintains a robust compliance posture with ISO certifications for operations across DoD Impact Levels 4 through 7. Complementing this, the Virtru Data Harbor Platform is built on the OpenTDF standard, holds FedRAMP Moderate authorization, and is validated against FIPS 140-3 key management requirements.
The integrated solution supports NIST SP 800-162 for Attribute-Based Access Control and NIST SP 800-207 for Zero Trust Architecture, while supporting NIST SP 800-53r5 standards for rigorous audit logging and traceability. Together, these platforms support the complex requirements of CMMC and the DoD Zero Trust Architecture, providing a verified security framework for both defense contractors and mission owners.
Privacy and data sovereignty
To preserve identity sovereignty, all entitlements remain within your organization’s chosen identity provider. The Virtru Data Harbor Platform evaluates these attributes from any OIDC/OAuth2-compatible IdP to enable granular, data-layer enforcement without centralizing sensitive user data. Because the Pexip Policy Enforcement Point only transmits the minimum data necessary for a policy decision, no raw entitlement values persist within the VTC platform.
Collaboration
Channel access that keeps up with your team. Virtru checks members against your identity provider, and revokes access once they no longer qualify.
Collaboration
Secure Matrix-based messaging with access that follows policy. Virtru governs who can join each room, and who can open the files shared inside it.
Collaboration
Mission-ready collaboration with Zero Trust file protection. A Virtru plugin decides who can upload and view files in each channel, wherever they travel.