Collaboration
Element
Secure Matrix-based messaging with access that follows policy. Virtru governs who can join each room, and who can open the files shared inside it.
Mission-ready collaboration. Zero Trust file protection.
Mattermost runs mission collaboration for sovereign and disconnected environments. Data Harbor Platform checks every file at upload and again at view.
How Mattermost and Data Harbor Platform work together, and what each one does.
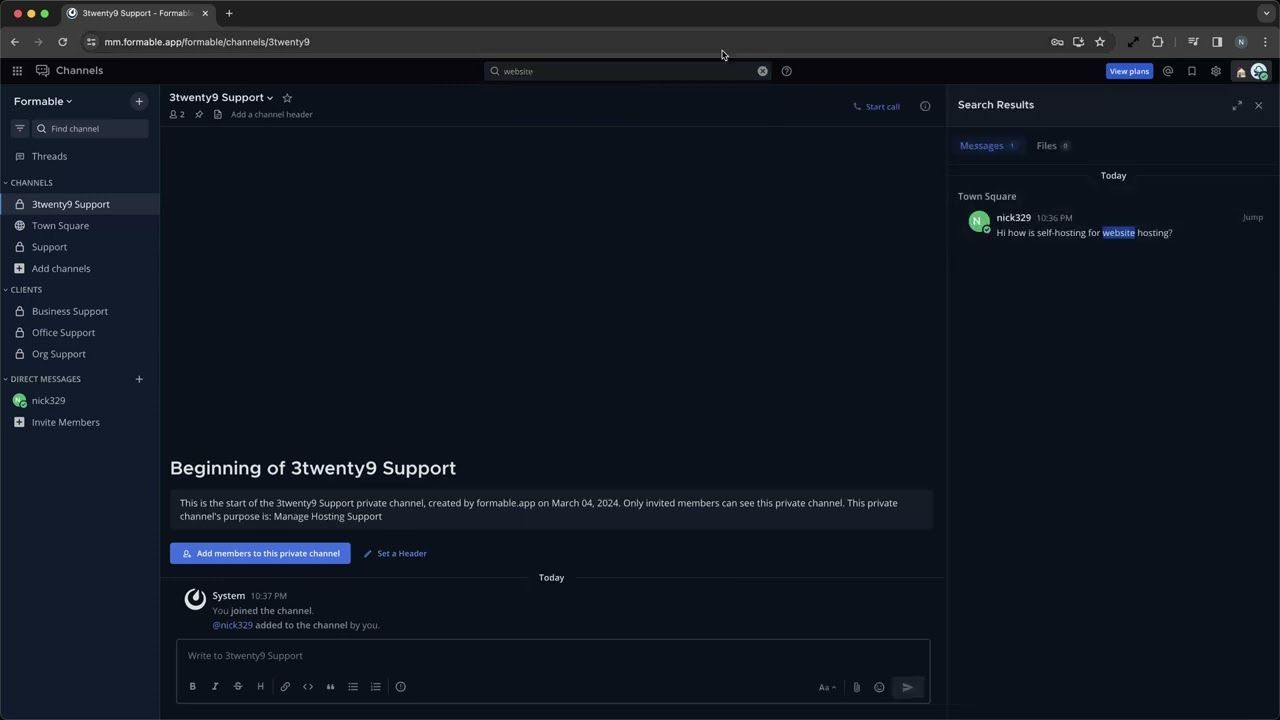
Mattermost is an Intelligent Mission Environment built specifically for national security, defense, intelligence, and critical infrastructure. Unlike general-purpose tools, it is designed for complete data sovereignty and operational control, deployable on-premises, in private cloud, or within disconnected, denied, intermittent, and limited (DDIL) environments.
Mattermost delivers persistent, encrypted team communication, including classification banners, data spillage prevention, role-based access control, and full audit trails across web, desktop, and mobile. Through Playbooks, our workflow automation codifies operational procedures into repeatable sequences, while AI-powered decision support connects to private or sovereign LLMs without external dependencies. Trusted by the U.S. Department of War, Air Force, NASA, and allied Five Eyes partners, the platform is co-built by over 4,000 contributors, meets DISA Impact Levels IL2-IL6, and offers FIPS 140-3 validated cryptography.
The Virtru integration operates via the Virtru ZTDF Bridge, a Mattermost plugin that designates the Virtru Data Harbor Platform as the Policy Decision Point for all file activity within Mattermost channels. When a file is uploaded, Mattermost verifies the user’s identity and attributes against central policies before accepting the file. Similarly, when a file is opened, Mattermost consults the Virtru PDP to evaluate the viewer’s clearance, role, and assignment before rendering the content natively. Users can securely view protected images, PDFs, text, audio, and video directly within the Mattermost interface, ensuring data remains within the controlled environment throughout its lifecycle.
Mattermost’s role-based access controls integrate seamlessly with the Virtru Policy Decision Point. Instead of relying on fragmented, per-channel rules, access is governed by a unified policy across all systems. This ensures that clearance and role attributes are evaluated consistently at both upload and view. Consequently, any access revocation takes effect in seconds across the entire data layer.
Furthermore, Mattermost’s DDIL (Disconnected, Denied, Intermittent, and Limited) architecture ensures continuity during operations. ZTDF protection is applied to files before they enter Mattermost, meaning that even in air-gapped or offline environments, files carry their access policies with them. In forward-deployed nodes without direct PDP connectivity, cryptographic protection remains active, ensuring that only authorized users can open the file, with audit records automatically syncing once connectivity is restored.
Together, Mattermost and Virtru provide a unique collaboration environment where the communication and data layers enforce policy independently. This synergy makes Mattermost the first collaboration platform to achieve data-centric Zero Trust protection at the file layer.
What you get when Mattermost and Data Harbor Platform run side by side.
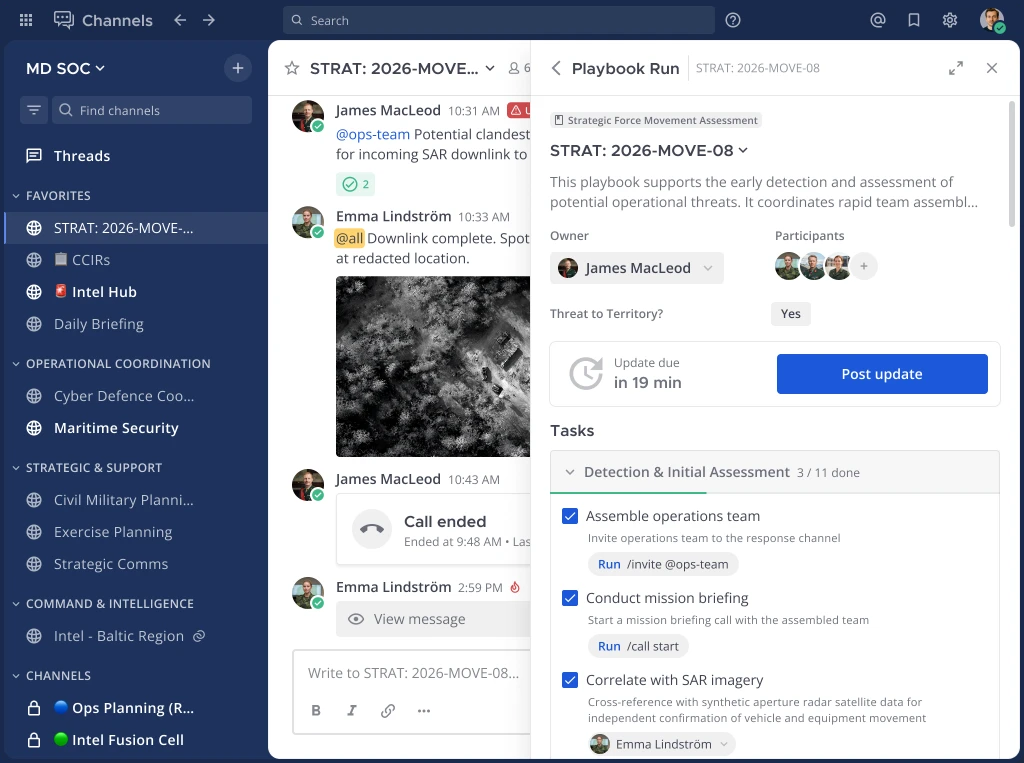
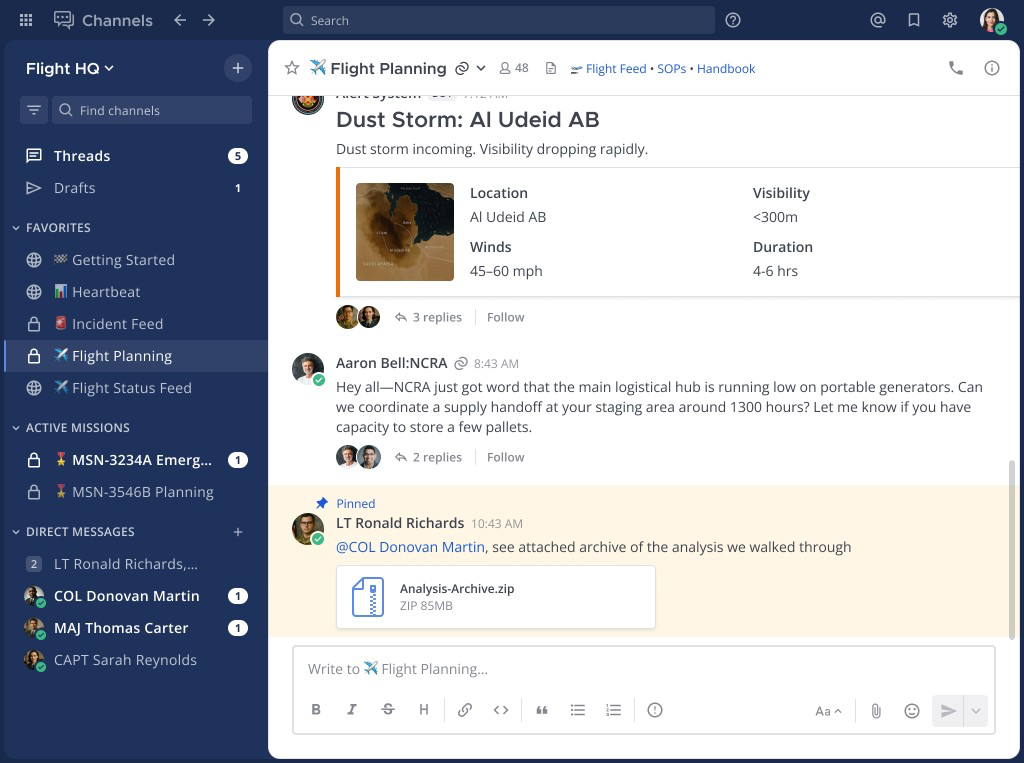
Offers persistent, encrypted messaging with classification banners, data spillage prevention, and role-based access controls. Operational across web, desktop, mobile, and air-gapped environments.
Codifies complex procedures into repeatable, automated workflows for incident response, mission planning, and compliance tracking.
Provides Kanban-style coordination enabling cross-functional teams to manage mission execution and maintain operational continuity.
Enables secure audio calls with transcription and AI-assisted summarization. Connects to private or sovereign LLMs without needing external dependencies.
Utilizes open APIs, webhooks, and a flexible plugin architecture with pre-built connectors for GitHub, GitLab, Jira, ServiceNow, TAK, Pexip, and other key systems.
Supports self-hosted on-premises or private cloud (AWS GovCloud, Azure Government, Oracle NSR) deployments. Designed for rapid field setup using Kubernetes or a single VM.
Provides dynamic, attribute-based access controls enforced via user attributes, clearance levels, and device posture. Fully supports DISA IL2-IL6.
Deploying the Virtru Data Harbor Platform with Mattermost requires an active Mattermost Enterprise Advanced deployment, a Virtru deployment, and an identity provider to source the user and environmental attributes that drive access decisions.
Required for the Virtru ZTDF Bridge plugin and advanced security controls.
Customer VPC, on-premises, or air-gapped; supports the same environmental profiles as Mattermost’s DDIL and disconnected deployments.
Installed and configured in the Mattermost admin console.
Okta, Microsoft Entra ID, Ping Identity, or equivalent, for ABAC attribute sourcing.
Between the Mattermost deployment and the Virtru PDP for online policy evaluation; offline mode available for DDIL environments.
How the two platforms split the work across security, compliance and privacy.
The Virtru Data Harbor Platform enhances Mattermost with object-level ZTDF encryption and attribute-based access control, ensuring security persists even after files leave the channel. Access policy is enforced independently at both upload and view, creating two distinct security decision points for every file interaction. This protection travels with the data, regardless of its destination. Decryption authority remains strictly with the data owner, and every access event, including user identity, attributes, policy context, and decision outcomes, is fully logged within both Mattermost and Virtru audit systems.
Compliance
Virtru’s Trusted Data Format (TDF) and OpenTDF, evolved from NSA-developed technology, provide persistent protection. Virtru supports ACP-240, the Five Eyes-ratified Zero Trust standard for coalition data sharing, alongside IC-TDF and NATO STANAG 5636. Complementing these data-layer protections, Mattermost meets DISA Impact Levels IL2-IL6, offers FIPS 140-3 validated cryptography, and provides STIG-compliant container images. Both organizations actively drive ACP-240 adoption to secure NATO and allied government missions.
Privacy
Your file content and encryption keys never leave your controlled environment, as the entire integration deploys within your accreditation boundary. Because you retain control of your own keys, decryption authority remains exclusively with you. Virtru enforces your access policies without ever accessing or holding your plaintext data.
Collaboration
Secure Matrix-based messaging with access that follows policy. Virtru governs who can join each room, and who can open the files shared inside it.
Collaboration
File sanitization paired with policy controls. Glasswall rebuilds each file clean, and Virtru keeps it encrypted and governed as it crosses domains.
Data
Data X-Ray finds sensitive files across your systems and labels them. Virtru reads those labels and encrypts each file automatically, before it moves.