AI
Kong AI Gateway
One gateway for AI traffic. One policy for the data behind it. Kong routes every request, and Virtru decides which records each agent can see.
Classification-enforced collaboration: the right people in the right conversations with access to the right data.
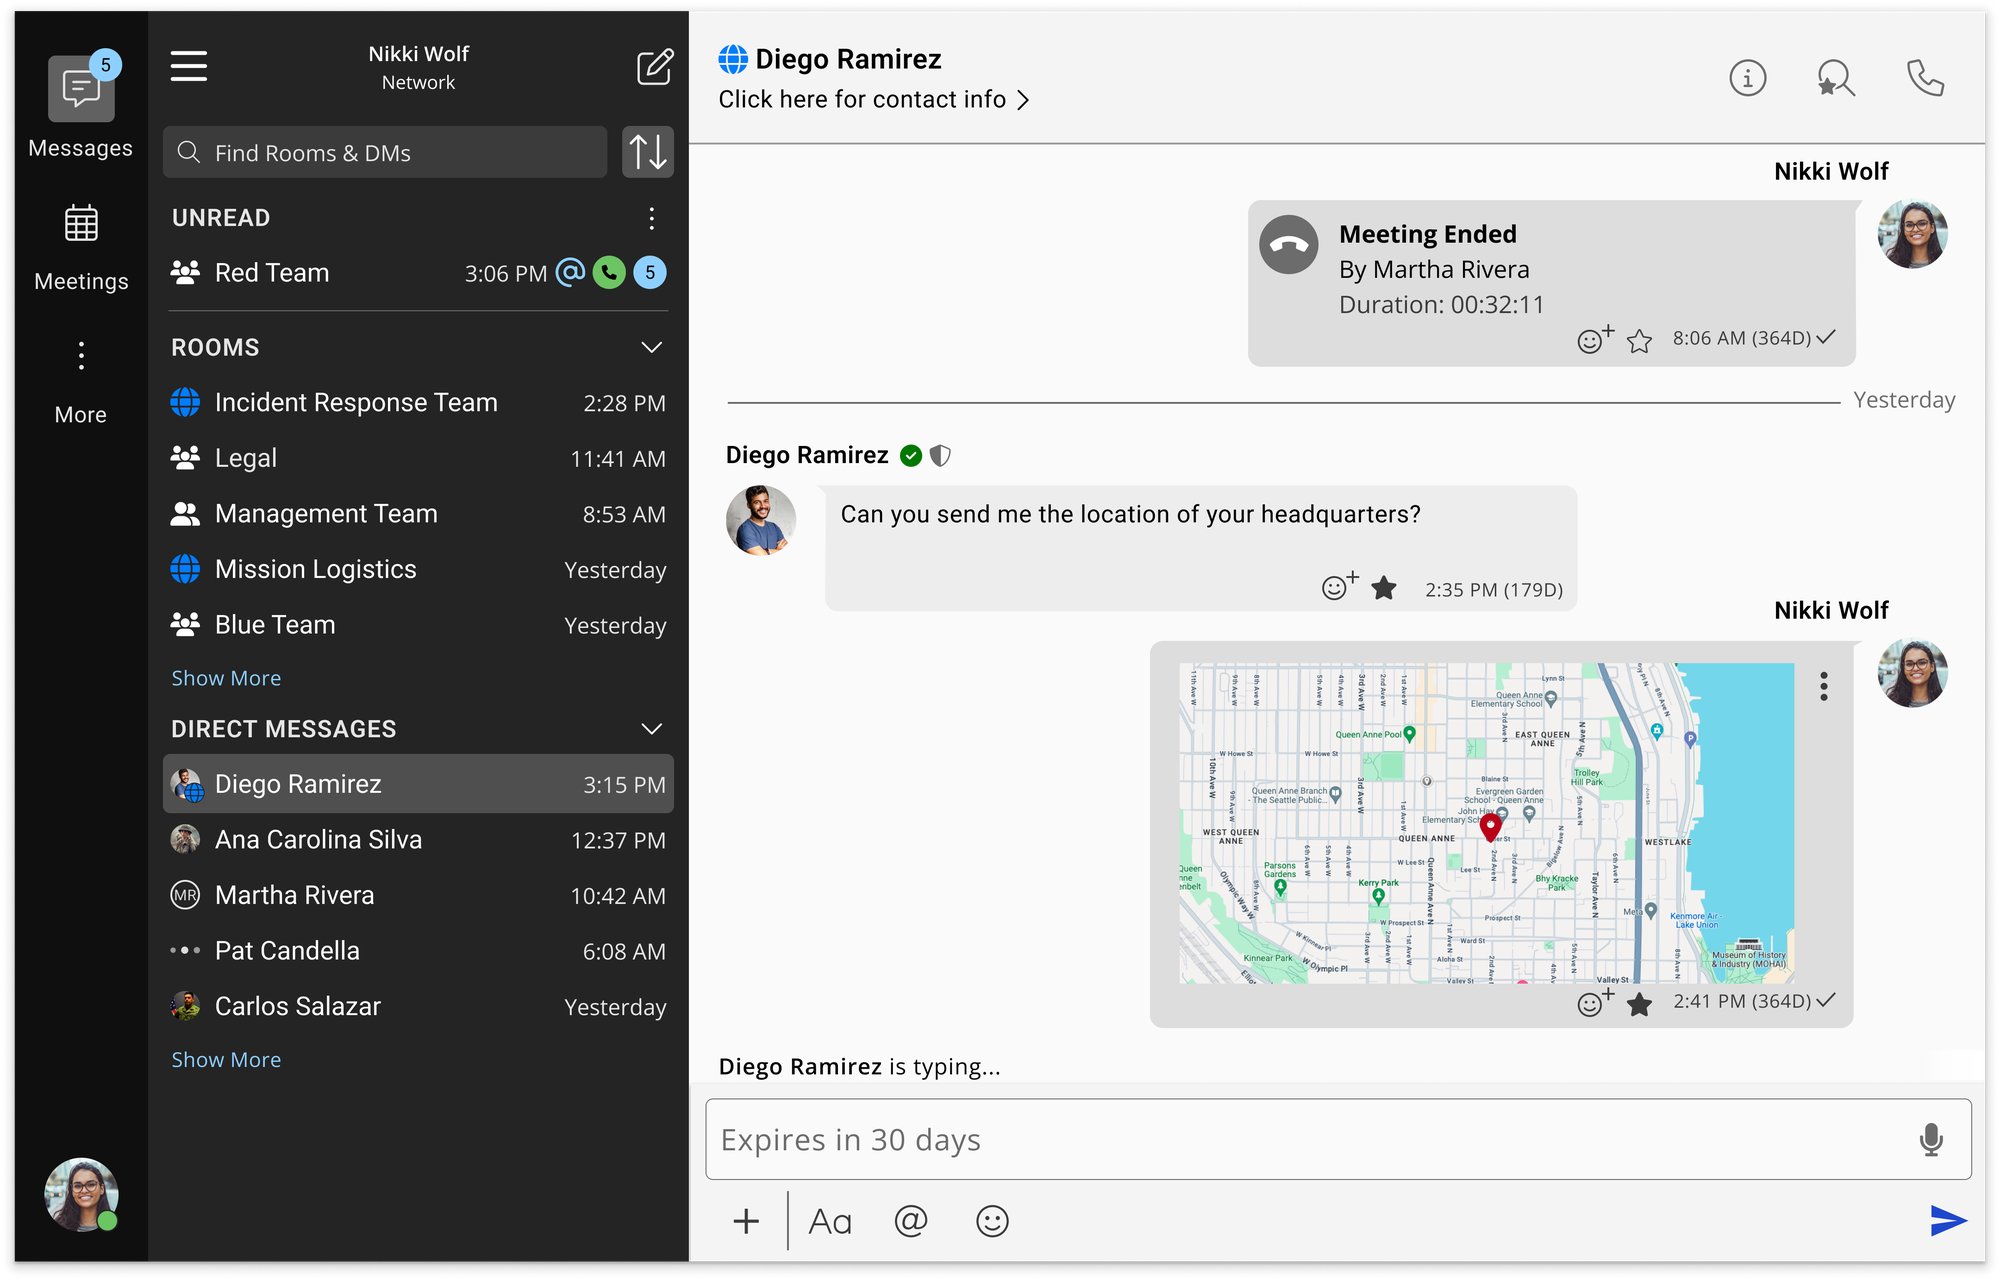
WickrGov encrypts every message, call and file. Data Harbor Platform decides who can join each room, and keeps checking while they stay.
How AWS WickrGov and Data Harbor Platform work together, and what each one does.
AWS WickrGov is a FedRAMP High and DoD IL5-authorized secure collaboration platform purpose-built for government, defense, and intelligence community environments. End-to-end encrypted messaging, voice and video calls, file sharing, and screen sharing, all running on a digitally sovereign design deployed in AWS GovCloud (US-West) and classified Regions, where even AWS cannot access your content.
What sets WickrGov apart is where it thrives. Ephemeral messaging with burn-on-read timers. Calls with up to 100 participants in restricted or disconnected environments. File transfers up to 5GB that work on low-bandwidth tactical networks. It’s purpose-built for scenarios where most collaboration tools fail, crisis response, classified operations, coalition coordination, and mission-critical communications at the edge.
How it works together
WickrGov secures the conversation. Virtru decides who belongs in it.
AWS WickrGov handles end-to-end encryption independently, messages, calls, and files are encrypted client-side with 256-bit encryption, and even AWS cannot access the content. That’s the encrypted channel. What WickrGov doesn’t do on its own is enforce dynamic, attribute-based access control at the room level. That’s where Virtru’s Data Harbor Platform comes in, data-layer enforcement with real-time ABAC, from first mile to last mile.
Virtru layers ABAC decisioning directly on top of WickrGov’s rooms. When a WickrGov room is classified, the Data Harbor Platform enforces that classification as a live access requirement, not a one-time gate. Users must meet the room’s classification attributes before they can join. Once inside, the platform continuously re-checks user attributes at configurable intervals and removes participants who no longer qualify. TDF-protected objects shared in a room are validated against the room’s classification before delivery. Protection travels with the data, policy portability that persists whether content stays in WickrGov or moves beyond it. The result: WickrGov owns the encrypted channel, Virtru owns the access decisions, and classification enforcement is continuous, not just at the door.
What you get when WickrGov and Data Harbor Platform run side by side.
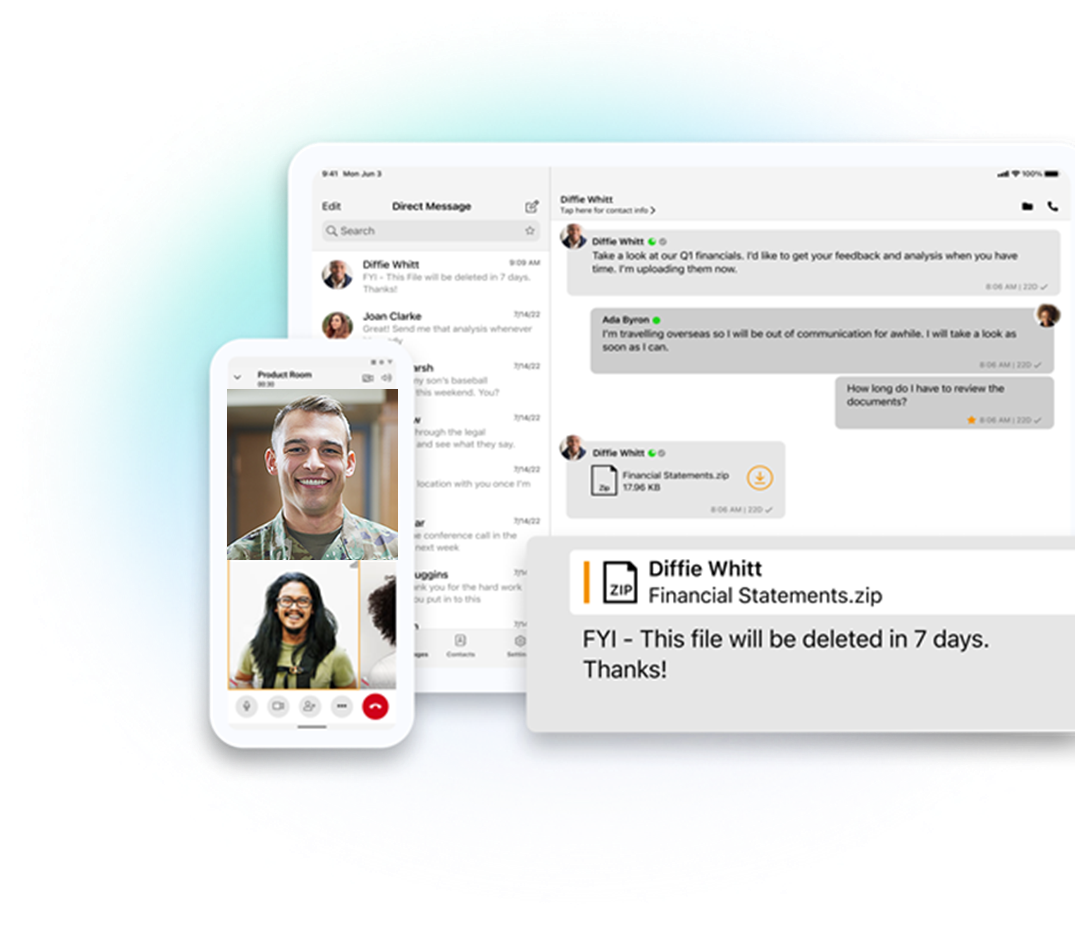
Messaging with expiration timers, burn-on-read, and screenshot detection; voice and video calls for up to 100 participants with presenter mode for 500; encrypted file sharing up to 5GB with view-only previews to reduce data loss risk.
For controlled collaboration with mission partners, coalition networks, and external organizations, with differentiated UX for out-of-network conversations and administrative control over federation rules.
With an always-on recipient (like BCC) that captures messages in a customer-hosted, self-decrypting archive, full compliance visibility without breaking end-to-end encryption.
Anticensorship capabilities that disguise traffic through global proxy servers, plus offline and degraded-network support for field, tactical, and disconnected environments.
Deploy self-hosted bots for automated workflows and mission system integrations; connect LLMs for AI-assisted collaboration, including air-gapped configurations where models run entirely within the secure network.
Replaces default TAK chat with WickrGov secure messaging, enabling encrypted comms and location sharing directly from the ATAK flywheel.
Deploying the AWS WickrGov and Virtru Data Harbor Platform integration requires active subscriptions to both platforms and a compatible identity infrastructure to enable attribute-based policy enforcement across the combined environment.
With an AWS WickrGov subscription.
Deployment (on-premises or virtual private cloud, air-gapped environments supported).
(e.g., Okta, Microsoft Entra ID, Ping Identity) for unified identity across both platforms.
For WickrGov administration and policy configuration.
Between WickrGov endpoints and Virtru Data Harbor Platform services (or local Data Harbor Platform deployment for air-gapped environments).
How the two platforms split the work across security, compliance and privacy.
WickrGov and Virtru handle distinct layers of the security stack. WickrGov provides 256-bit end-to-end encryption for all communications, messages, calls, and file transfers, encrypting them client-side with keys that only intended recipients possess. Virtru Data Harbor Platform operates at the access control layer, enforcing classification-based ABAC policies on WickrGov rooms. This includes verifying join-time attributes, continuously re-evaluating participant eligibility, and matching TDF classifications before objects are delivered. Integration, not replacement, neither platform depends on the other for its core security function, and encryption and access control operate independently.
Compliance
AWS WickrGov holds FedRAMP High authorization and DoD IL2, IL4, and IL5 accreditation, deployed in AWS GovCloud (US-West) and classified Regions. Virtru Data Harbor Platform maintains FedRAMP Moderate authorization, SOC 2 Type II, and HIPAA compliance. The Data Harbor Platform also supports IC-TDF for intelligence community workflows, ACP-240, and NATO STANAG 5636 for coalition operations, standards that carry through to the joint integration. Both platforms support FIPS 140-3 validated cryptographic modules.
Privacy
Zero-knowledge architecture on both sides. AWS cannot decrypt WickrGov communications, encryption keys are held only by intended recipients. Virtru Data Harbor Platform enforces a zero-trust architecture through its built-in KAS (Key Access Service), managing keys and access decisions for TDF-protected objects in WickrGov rooms. Key management supports AWS KMS for software-based workflows or Thales HSMs for on-premises deployments in air-gapped environments. User attributes used to drive ABAC decisions are evaluated in real time without exposing identity data to WickrGov. No vendor backdoors, no split-key compromises.
AI
One gateway for AI traffic. One policy for the data behind it. Kong routes every request, and Virtru decides which records each agent can see.
Collaboration
Channel access that keeps up with your team. Virtru checks members against your identity provider, and revokes access once they no longer qualify.
Collaboration
Sovereign video meetings, governed end to end. Virtru checks policy when a meeting is scheduled, and again as each person joins the call.